Create Virtual Private Gateway
Create Virtual Private Gateway (VGW)
ℹ️ Overview
- A Virtual Private Gateway (VGW) is a key component for Site-to-Site VPN connections.
- It acts as the AWS-side VPN endpoint.
- It must be attached to the target VPC before establishing the VPN connection.
Steps to Implement
- Open the AWS VPC Console
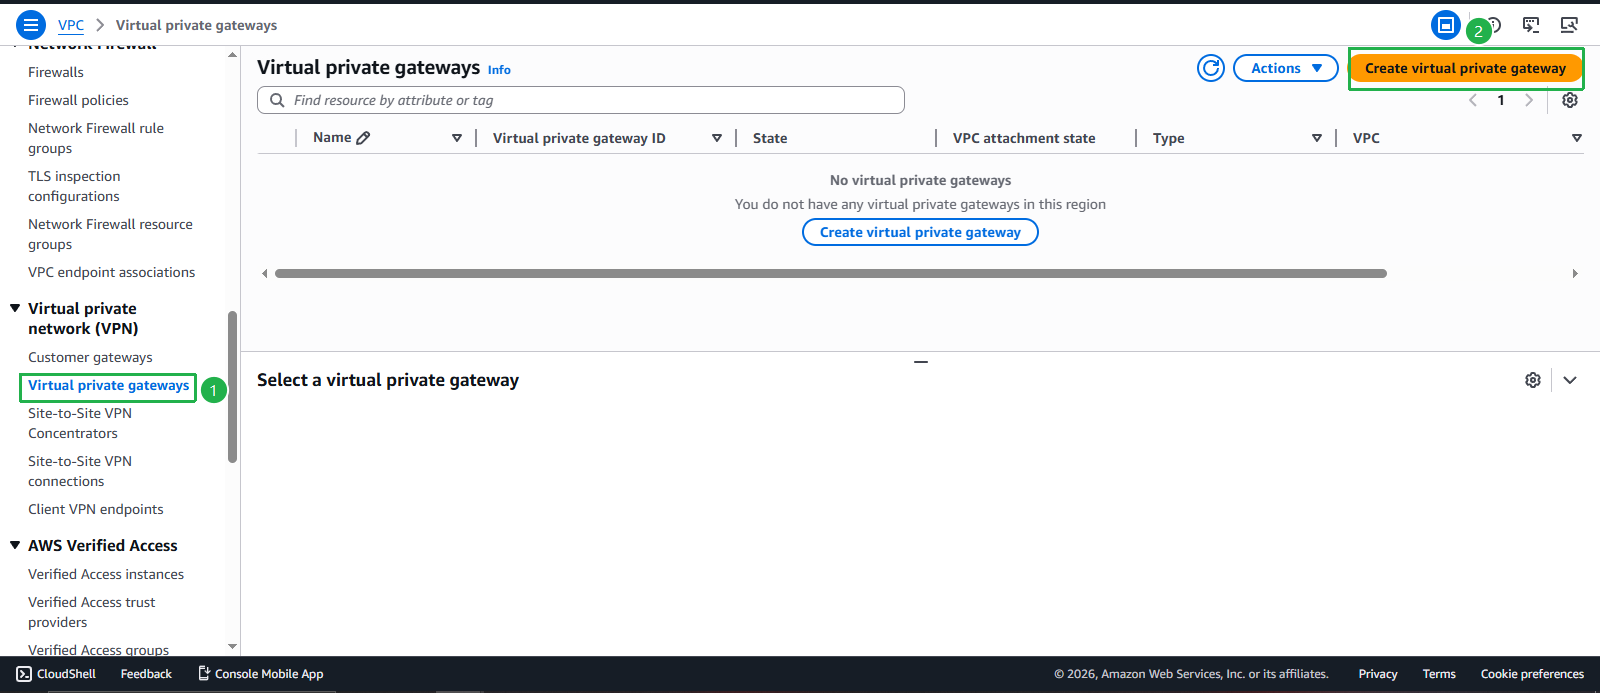
- Navigate to Virtual Private Gateways
- Click Create Virtual Private Gateway

Configure the Virtual Private Gateway
- Name tag: Enter
VPN Gateway - ASN: Select Amazon default ASN
- Click Create virtual private gateway
💡 ASN Explanation:
- Amazon default ASN (64512): Suitable for most use cases
- Custom ASN: Only needed for advanced BGP routing with specific ASN requirements
- Name tag: Enter

- Attach the VGW to your VPC
- Click Actions
- Select Attach to VPC
Select the target VPC
- From the dropdown, choose VPC ASG (10.10.0.0/16)
- Click Attach to VPC
⚠️ Important: Attach to the MAIN VPC (ASG), not the VPN VPC!
- Verify status
- Check the State field — it should display Attached
- The VGW is now ready for the next VPN configuration steps
🏗️ Virtual Private Gateway Role
AWS VPC (10.10.0.0/16)
    ↓
Virtual Private Gateway (VGW)
    ↓
VPN Tunnel (IPsec)
    ↓
Customer Gateway (On-premises)
💡 Key Concepts:
- VGW: AWS-managed VPN concentrator
- Highly Available: Automatically deployed across multiple AZs
- Supports: Multiple VPN connections
- Routing: Can propagate routes to route tables
✅ Completed: Virtual Private Gateway is attached and ready!