Create EC2 Instance
Deploy EC2 Instance for Customer Gateway
ℹ️ Overview
- In this section, we will deploy an EC2 instance to act as the Customer Gateway.
- The instance will be placed in the public subnet of the ASG VPN VPC.
- A properly configured security group is required for VPN and SSH access.
Create Security Group
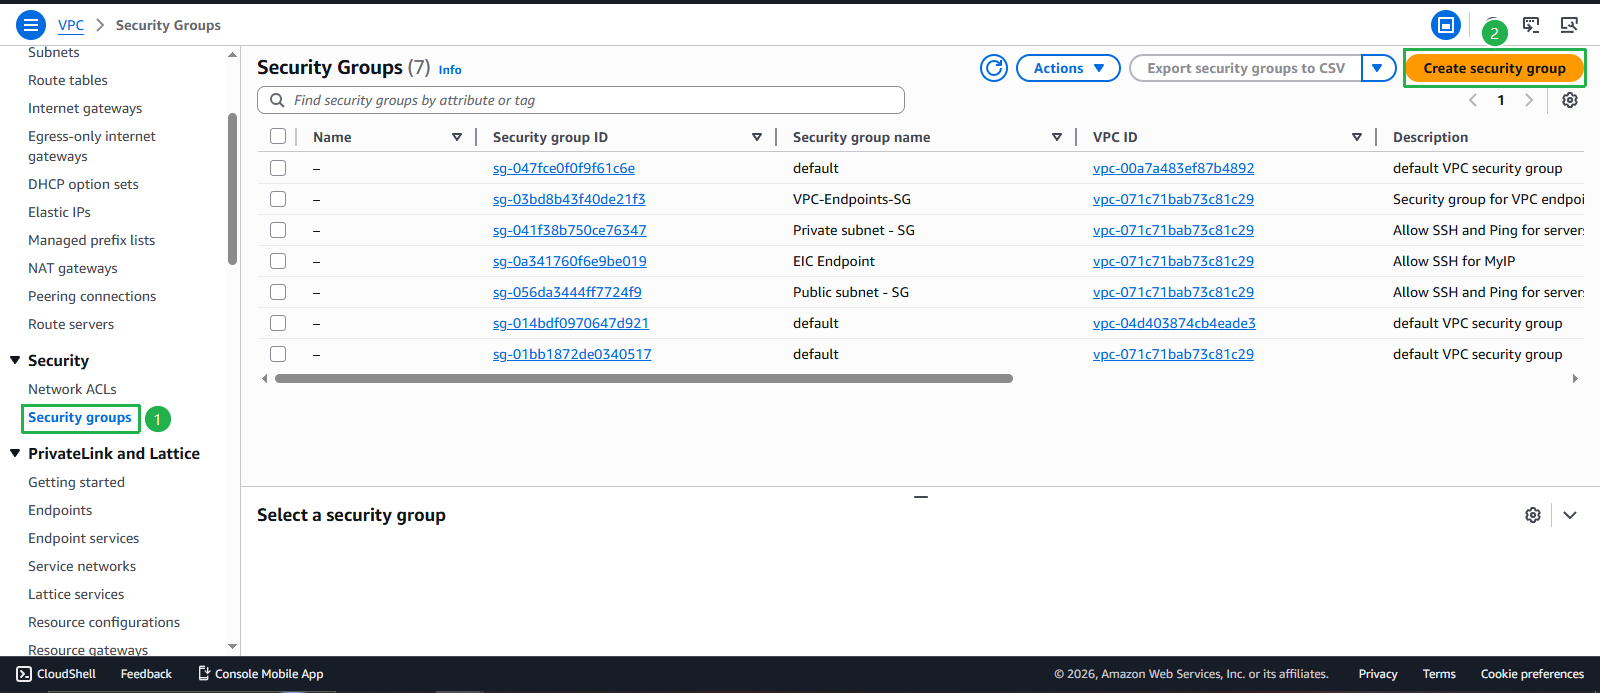
- Navigate to the VPC Dashboard
- Select Security Groups
- Click Create security group

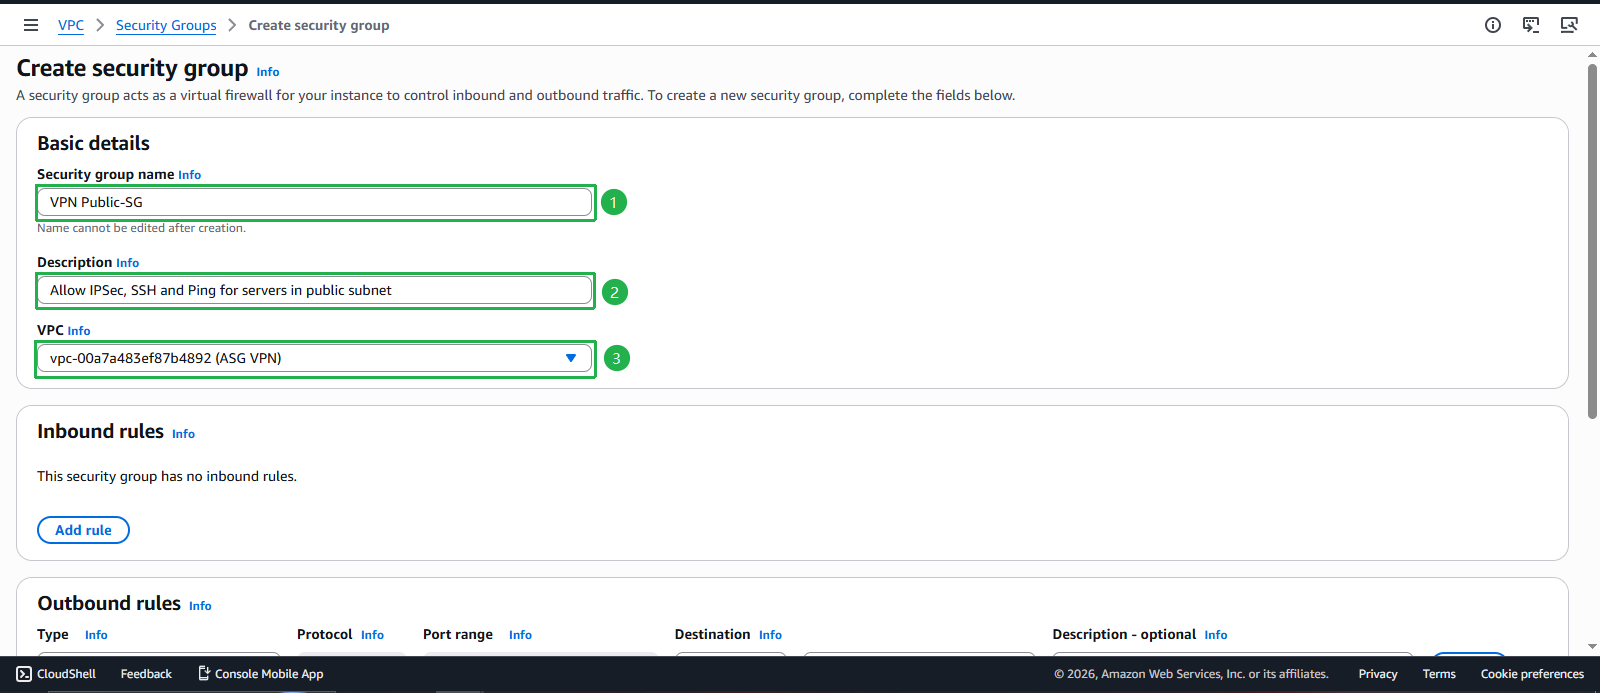
- Configure the Security Group
- Name: Enter
VPN Public-SG - Description: Enter
Allow IPSec, SSH and Ping for servers in public subnet - VPC: Select ASG VPN
- Name: Enter

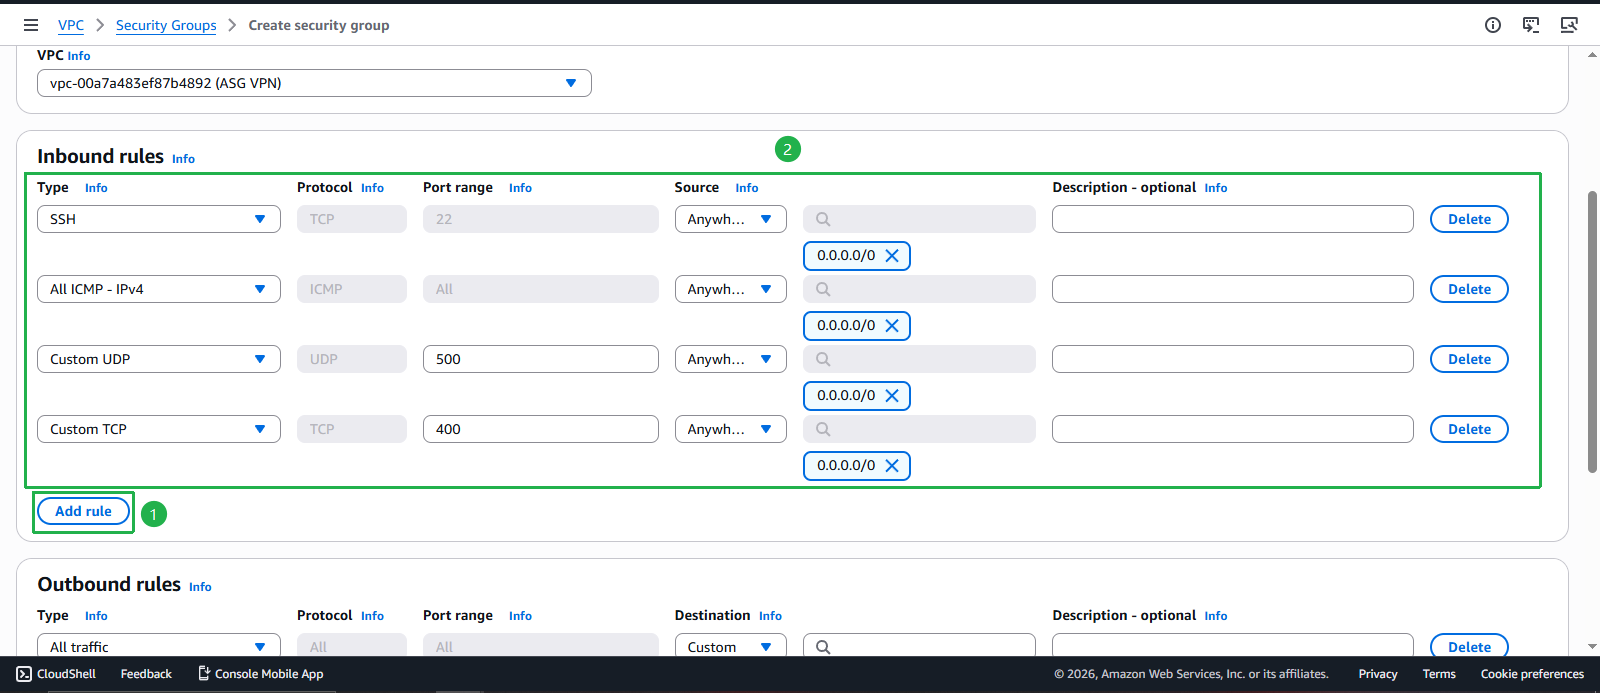
🔒 Security Rules - Inbound
Add the following inbound rules to support VPN and management:
| Type | Protocol | Port | Source | Purpose |
|---|---|---|---|---|
| SSH | TCP | 22 | My IP | Remote management |
| ICMP | ICMP | All | Anywhere | Ping testing |
| Custom UDP | UDP | 500 | Anywhere | IKE (IPsec key exchange) |
| Custom UDP | UDP | 4500 | Anywhere | NAT-T (IPsec NAT traversal) |
💡 Port Explanation:
- Port 500 (UDP): IKE (Internet Key Exchange) - Establishes VPN tunnel
- Port 4500 (UDP): NAT-T - IPsec through NAT devices
- ICMP: Allows ping for connectivity testing

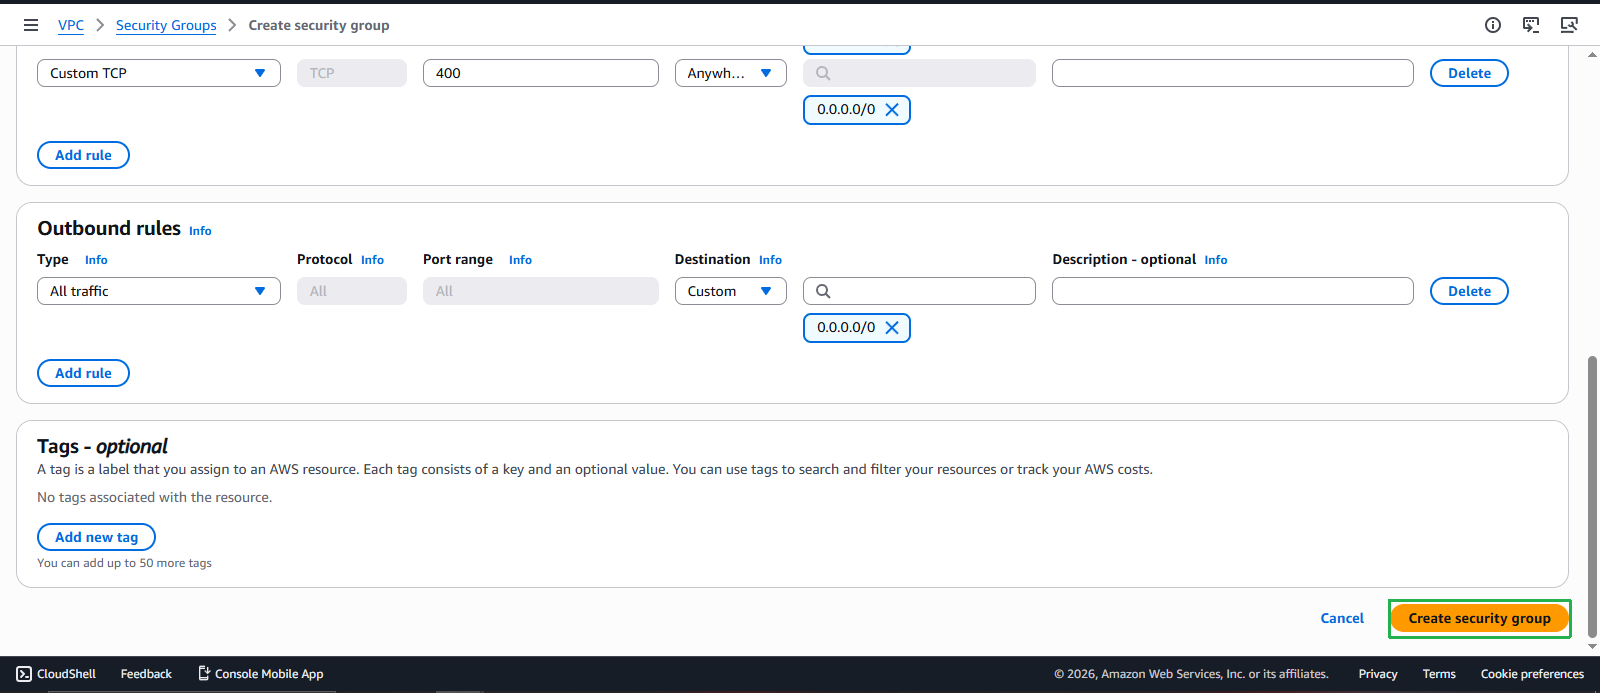
- Verify outbound rules and click Create security group
Deploy the EC2 Instance
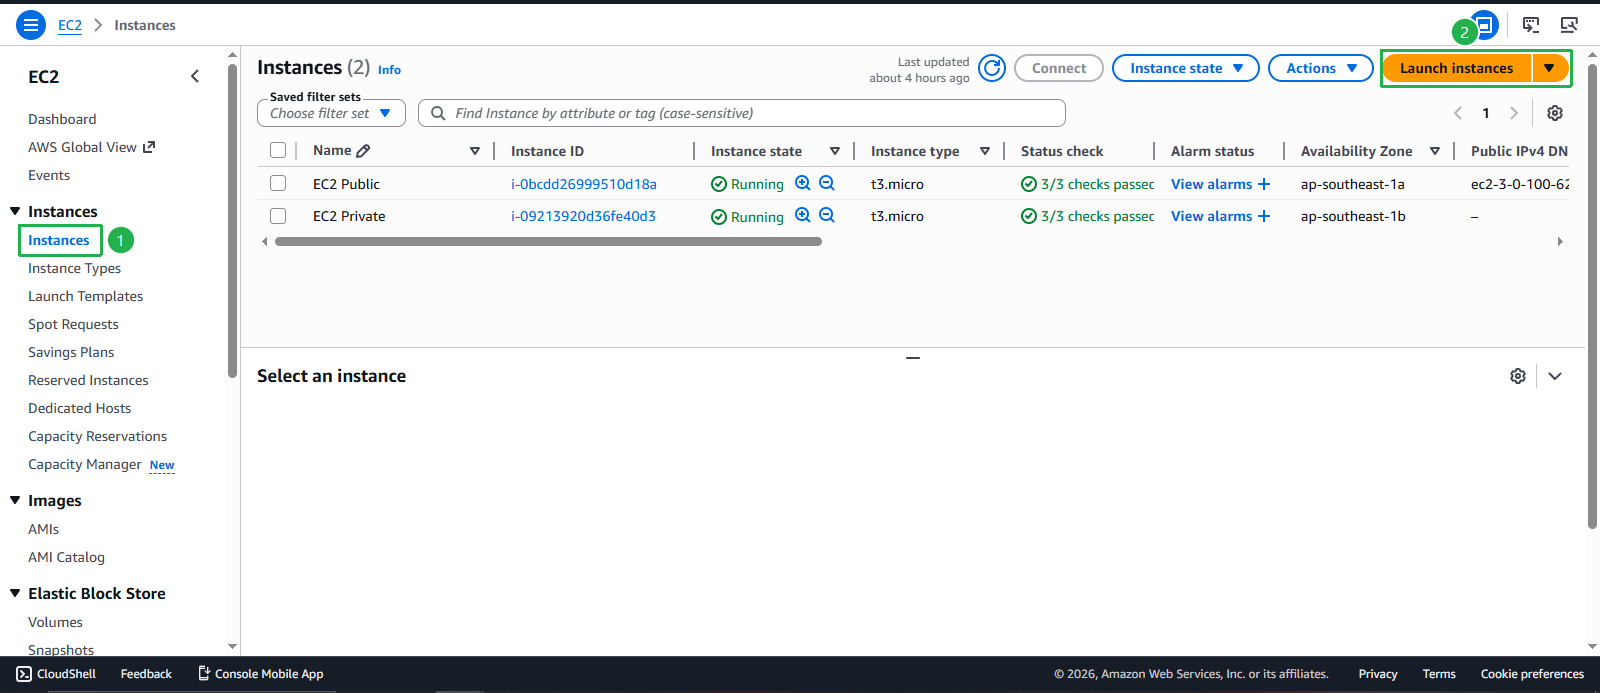
- Open the EC2 Dashboard
- Select Instances
- Click Launch instances
Configure the Instance
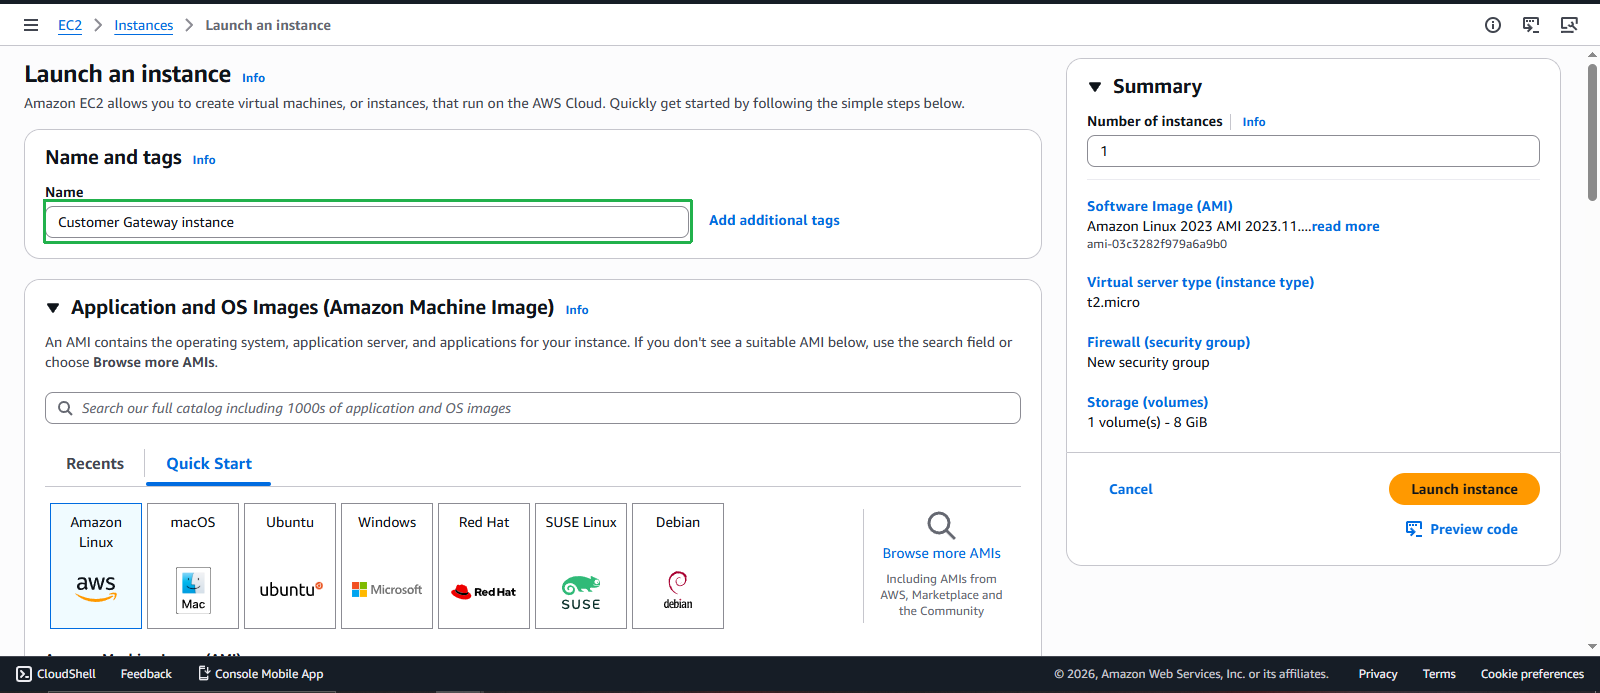
- Name: Enter
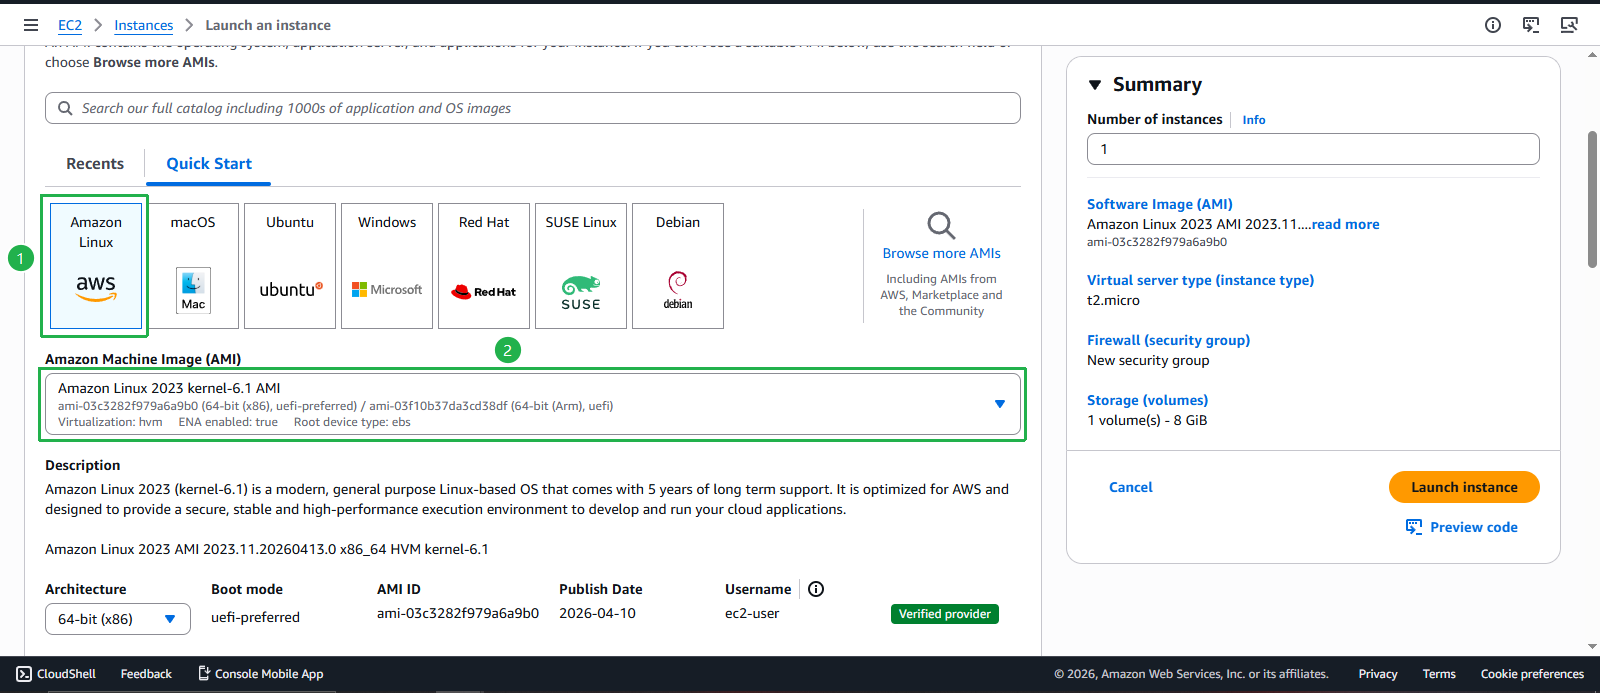
Customer Gateway instance - AMI: Select Amazon Linux 2023
- Instance type:
t3.micro - Key pair: Select
aws-keypair
💡 Instance Type Selection: t3.micro is sufficient for lab VPN gateway, production should use t3.small or larger.
- Name: Enter
Network Settings
- VPC: Select ASG VPN
- Subnet: Choose VPN Public
- Auto-assign public IP: Enable (Required for VPN)
- Security group: Select VPN Public-SG
Review and Launch Instance
- Double-check all configurations
- Click Launch instance
🏗️ Customer Gateway Role
Customer Gateway EC2 Instance
├── Libreswan/OpenSwan (IPsec software)
├── Public IP (VPN endpoint)
├── Private IP (10.11.1.x)
└── Routing configuration
⚠️ Important Notes
- ✅ Instance MUST have a public IP to establish VPN tunnel
- ✅ Security group must open ports 500 and 4500 (UDP) for IPsec
- ✅ Will need to disable source/destination check (next step)
- ✅ Save the Public IP for Customer Gateway configuration
💡 Next Steps: After the instance is running, we will:
- Disable source/destination check
- Install Libreswan
- Configure IPsec tunnels
✅ Completed: Customer Gateway EC2 is ready for VPN configuration!