Customizing AWS VPN Tunnel
Customizing AWS VPN Tunnel
ℹ️ Overview This section guides you through customizing VPN tunnel options and enabling logging to monitor VPN activity.
🏗️ Architecture Overview
┌─────────────────────────────────────────────────────────────┐
│                    VPN Tunnel Monitoring                     │
│                                                             │
│  ┌──────────────────┐    ┌─────────────────────────────┐   │
│  │   AWS Console    │    │      CloudWatch Logs       │   │
│  │                  │    │                             │   │
│  │ • Modify Tunnel  │───▶│ • Tunnel Activity Logs     │   │
│  │ • Configure DPD  │    │ • Connection Events        │   │
│  │ • Set Encryption │    │ • Authentication Logs      │   │
│  │ • Enable Logging │    │ • Performance Metrics      │   │
│  └──────────────────┘    └─────────────────────────────┘   │
│                                                             │
│  ┌──────────────────────────────────────────────────────┐  │
│  │              VPN Tunnel Options                      │  │
│  │                                                      │  │
│  │ • DPD Timeout: 30s (customizable)                   │  │
│  │ • IKE Version: IKEv1/IKEv2                          │  │
│  │ • Encryption: AES128/256, AES-GCM                   │  │
│  │ • Integrity: SHA1/SHA2-256/384/512                  │  │
│  │ • DH Groups: 2, 14-24                               │  │
│  └──────────────────────────────────────────────────────┘  │
└─────────────────────────────────────────────────────────────┘
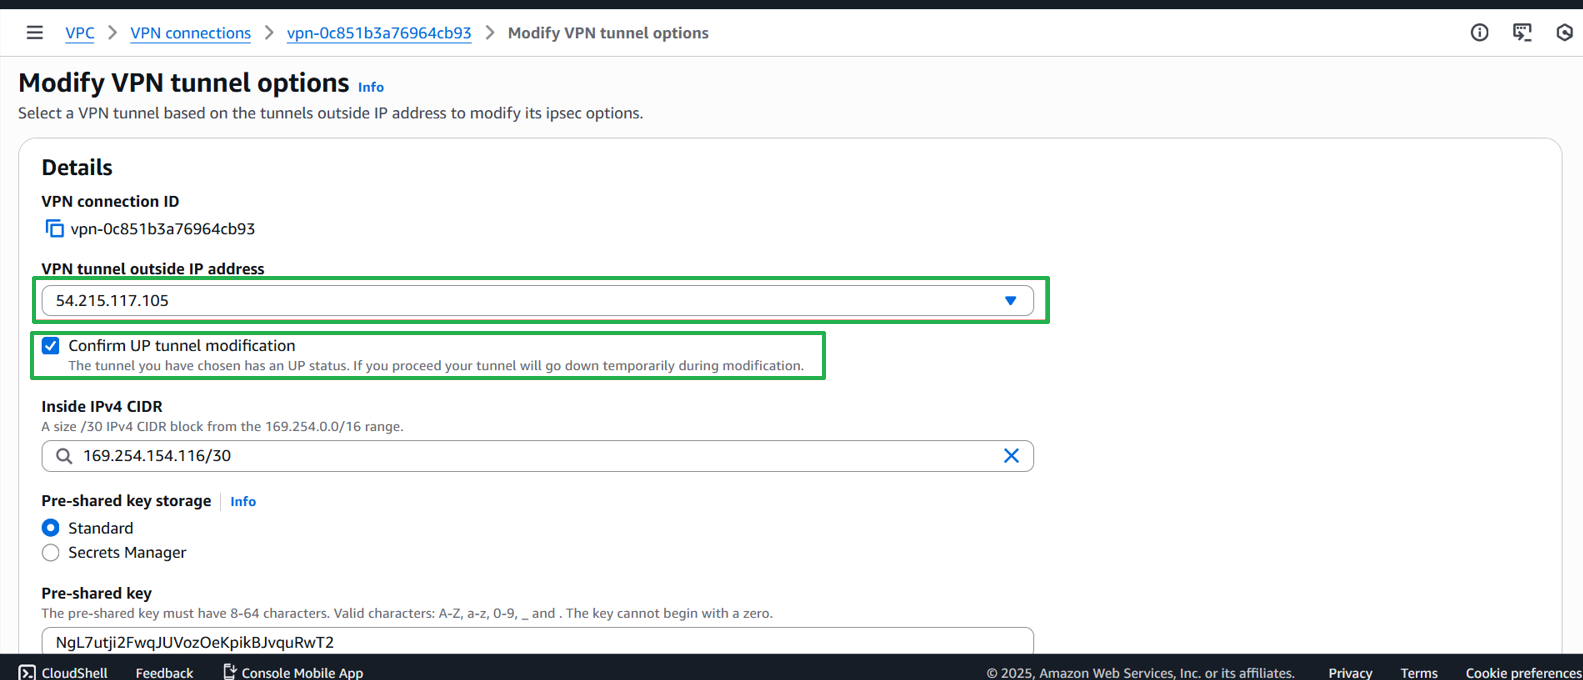
Access the VPC console
- Select Site-to-Site VPN Connections
- Select the VPN you just created
- Click Actions
- Select Modify VPN Tunnel Options
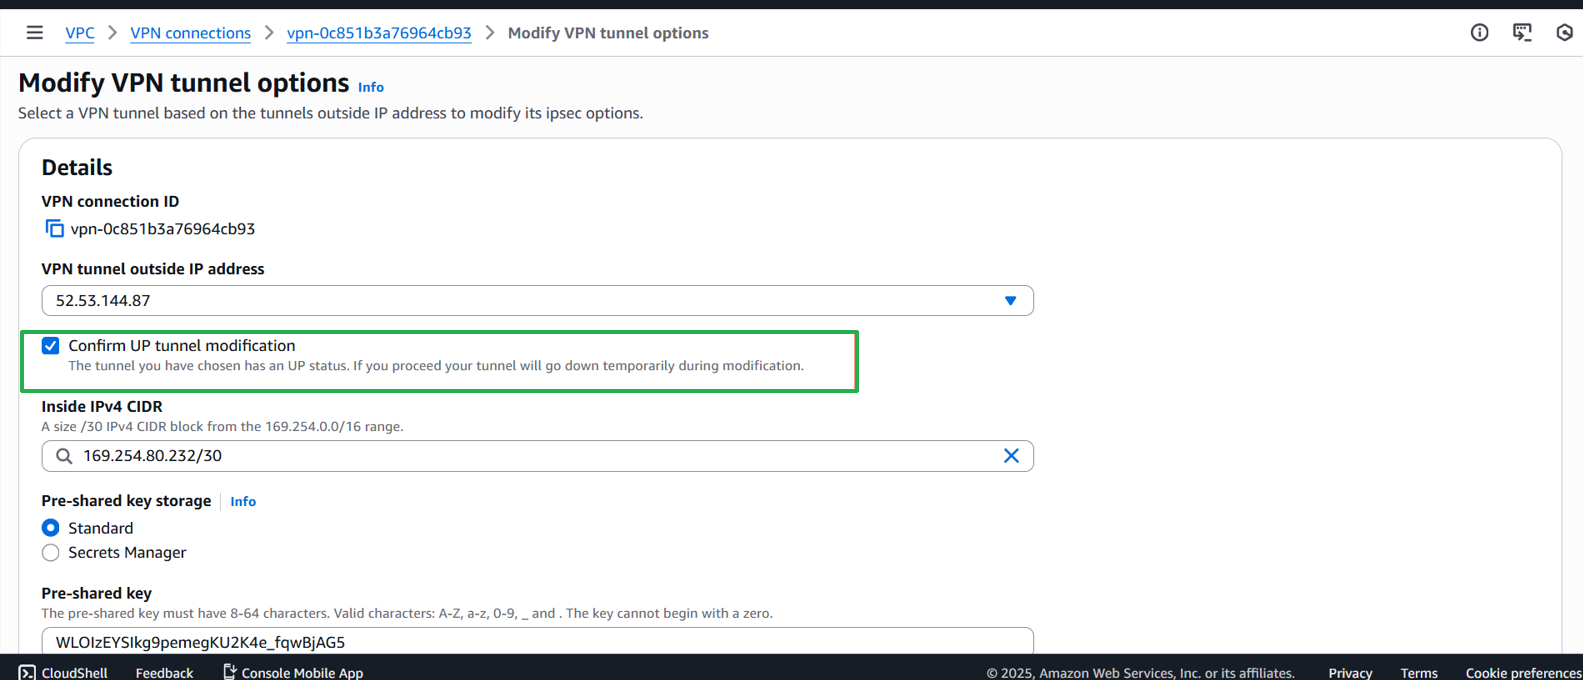
- Choose VPN Tunnel Outside IP Address
Click Confirm UP Tunnel Modification and keep default settings.
💡 Note: You can customize parameters like DPD timeout, IKE versions, encryption algorithms
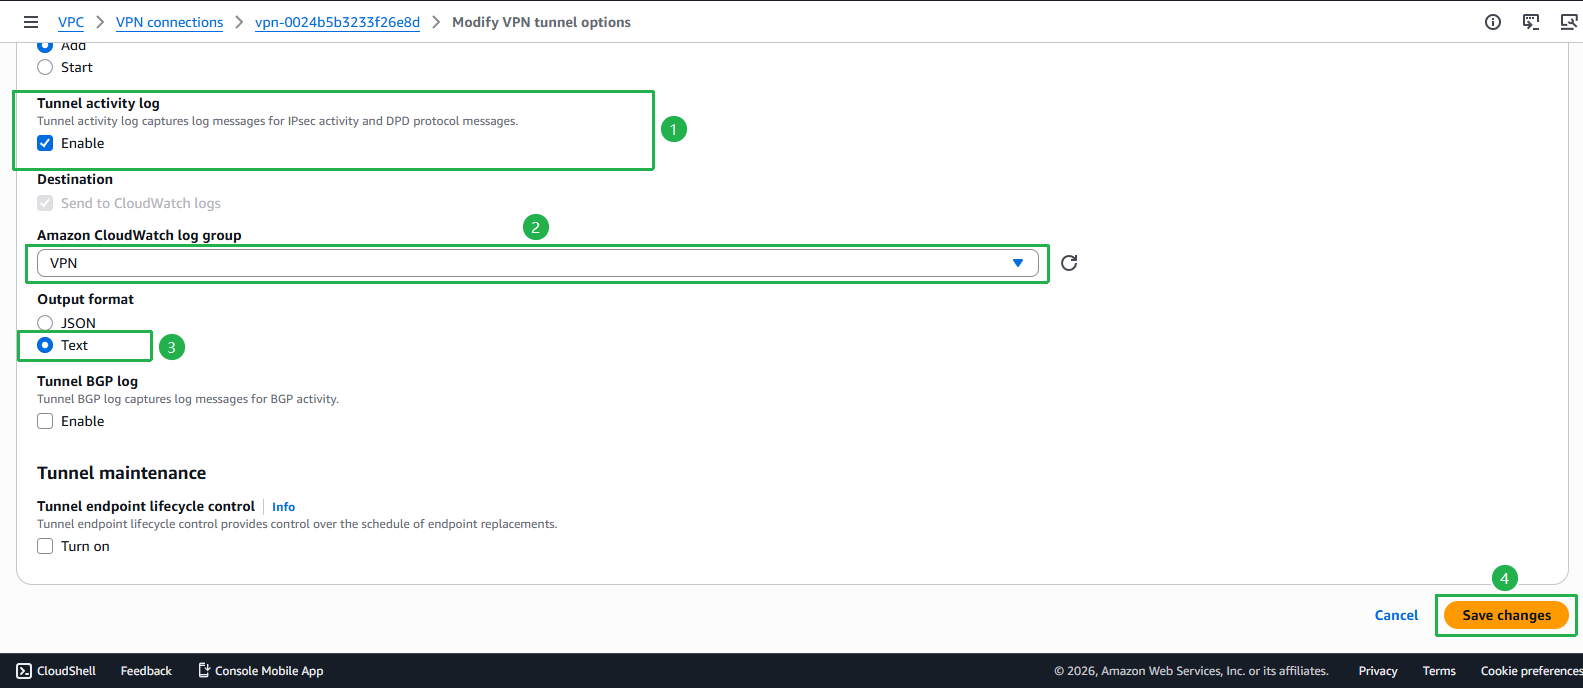
For Tunnel Activity Log, enable logging:
- Select Amazon CloudWatch Log Group (create one if it doesn’t exist)
- For Output Format, select Text or JSON
- Click Save Changes
🔍 Logging Benefits: Helps with troubleshooting, auditing, and monitoring VPN tunnel activity
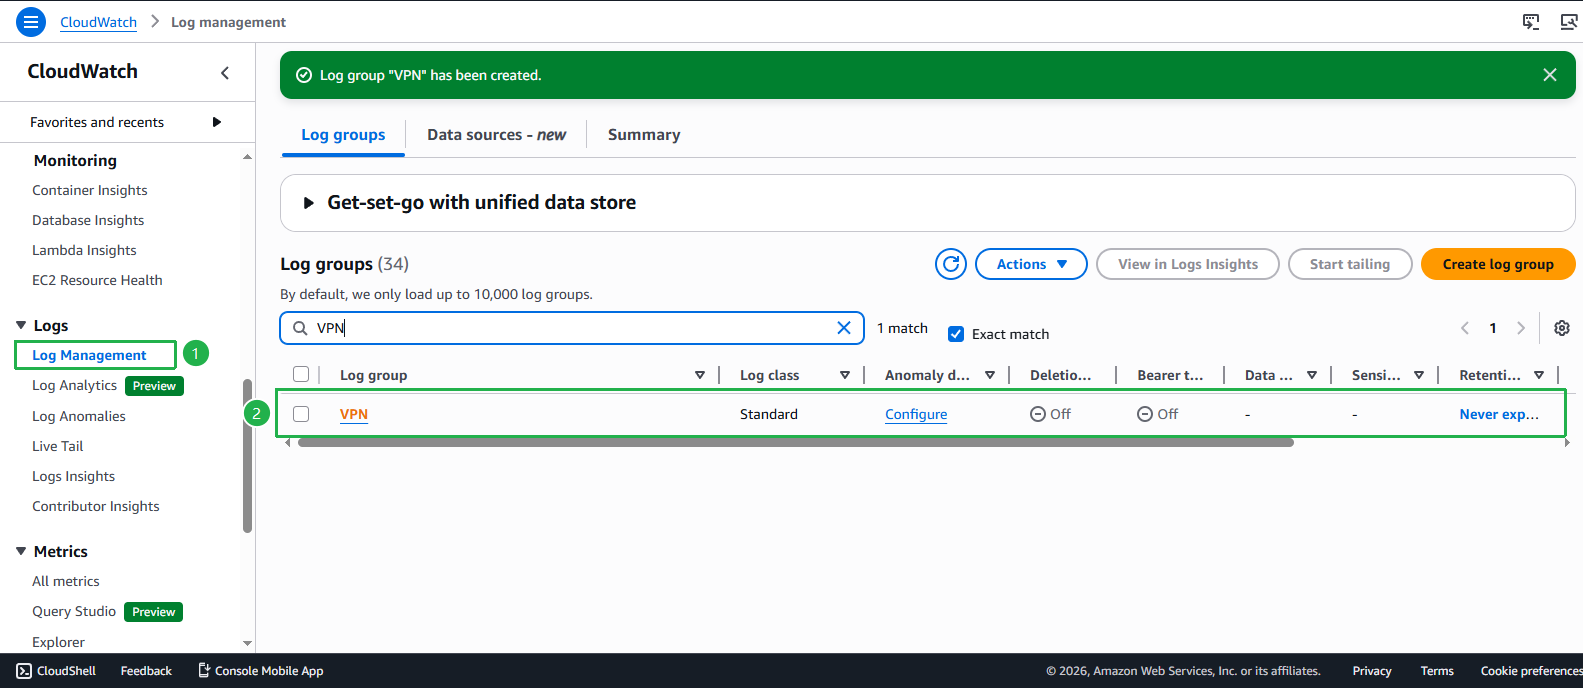
- Access CloudWatch
- Select Log Groups
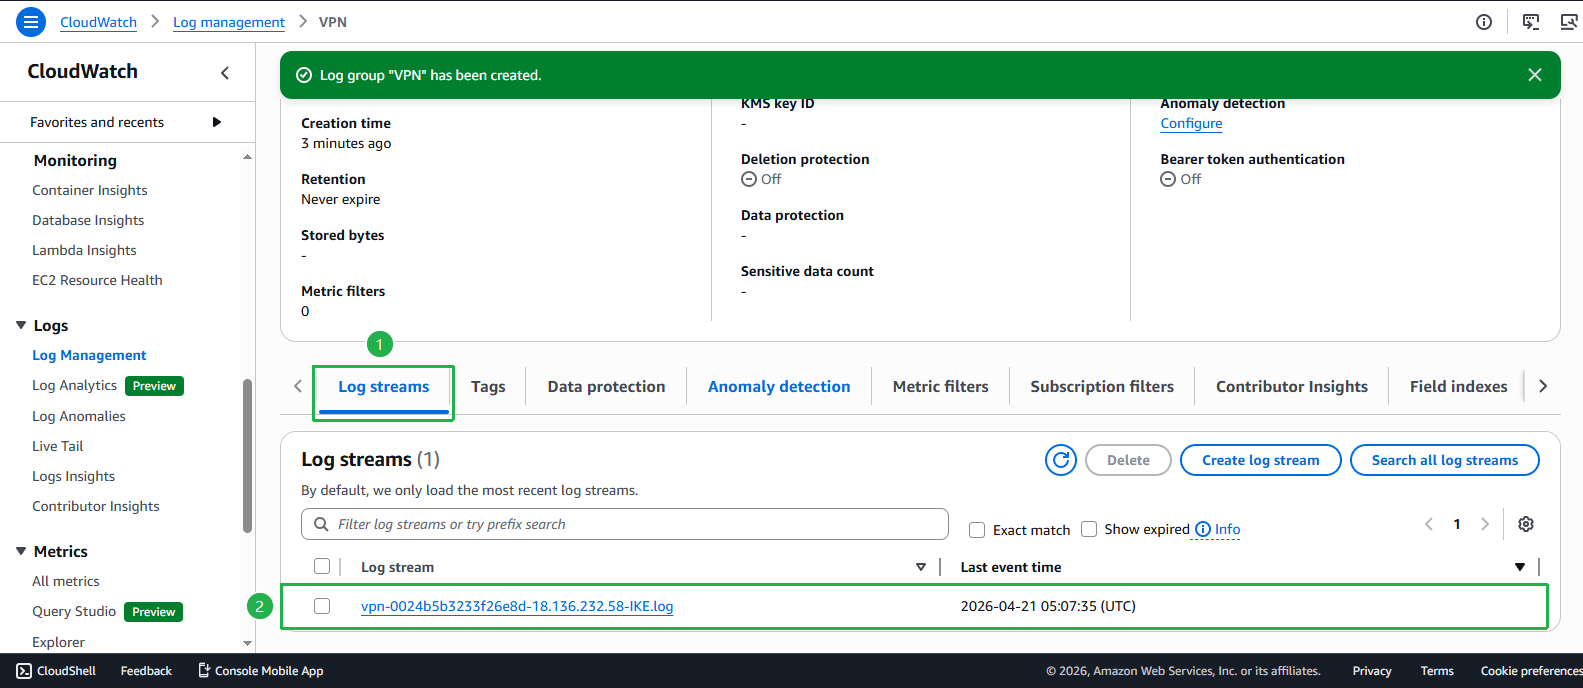
- Select Log Streams
- Open a stream to view logs
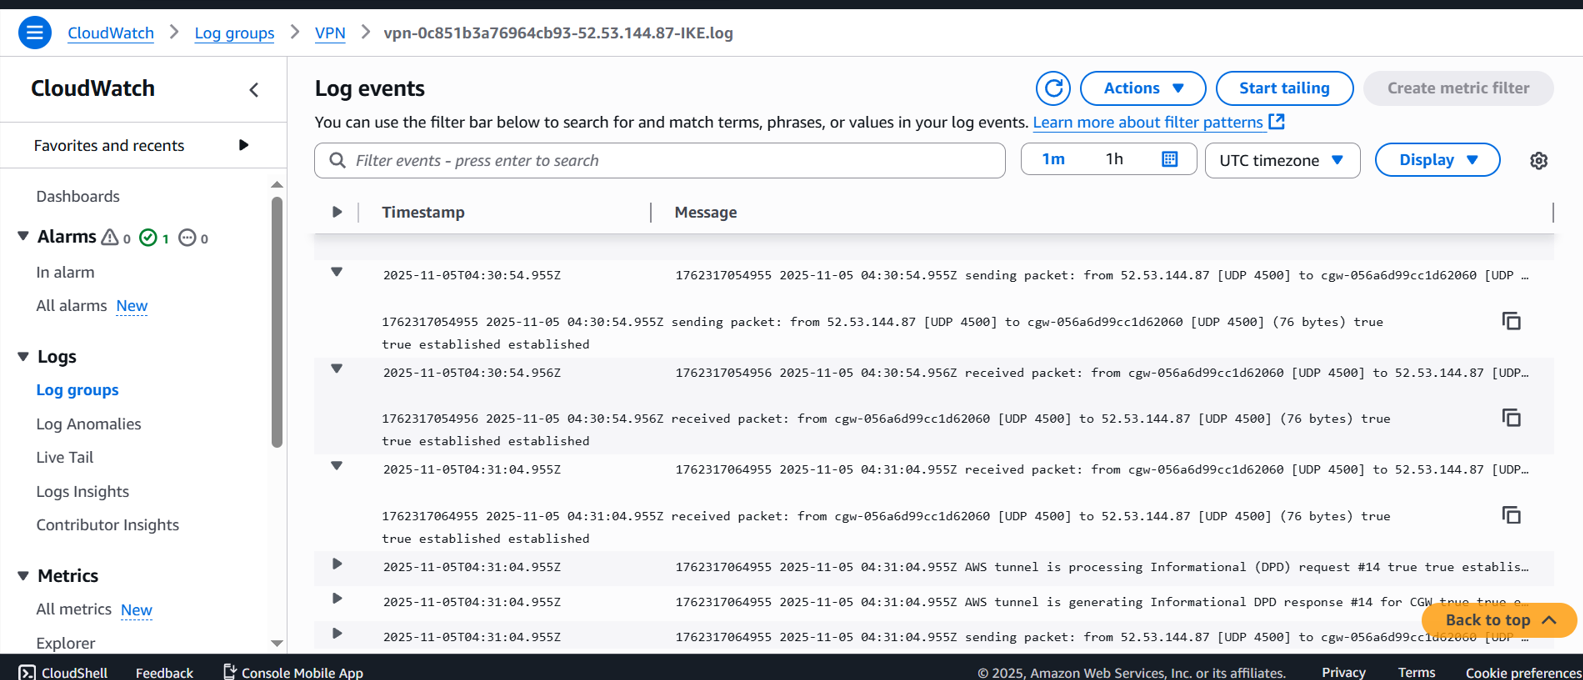
- View Log Events - detailed tunnel activity
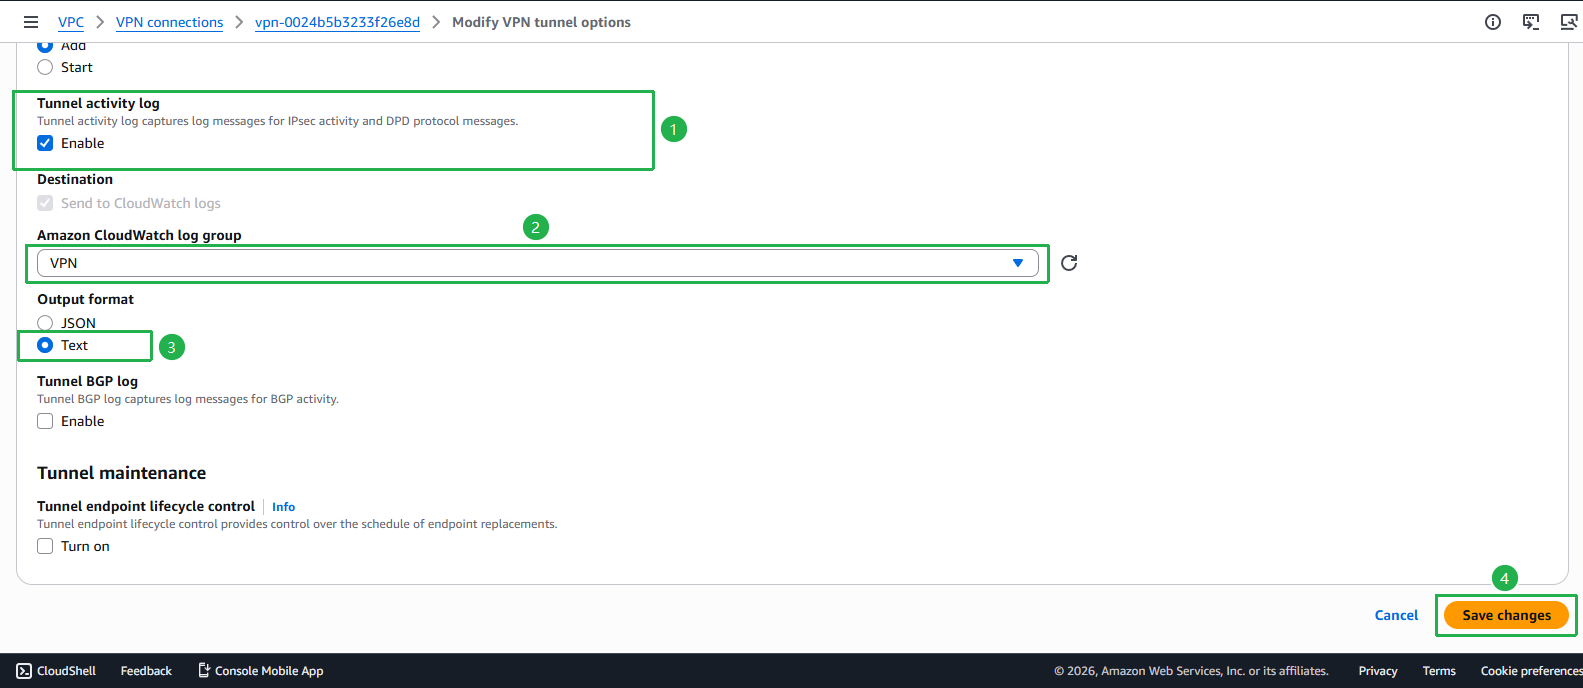
- Repeat the same procedure for the other tunnel
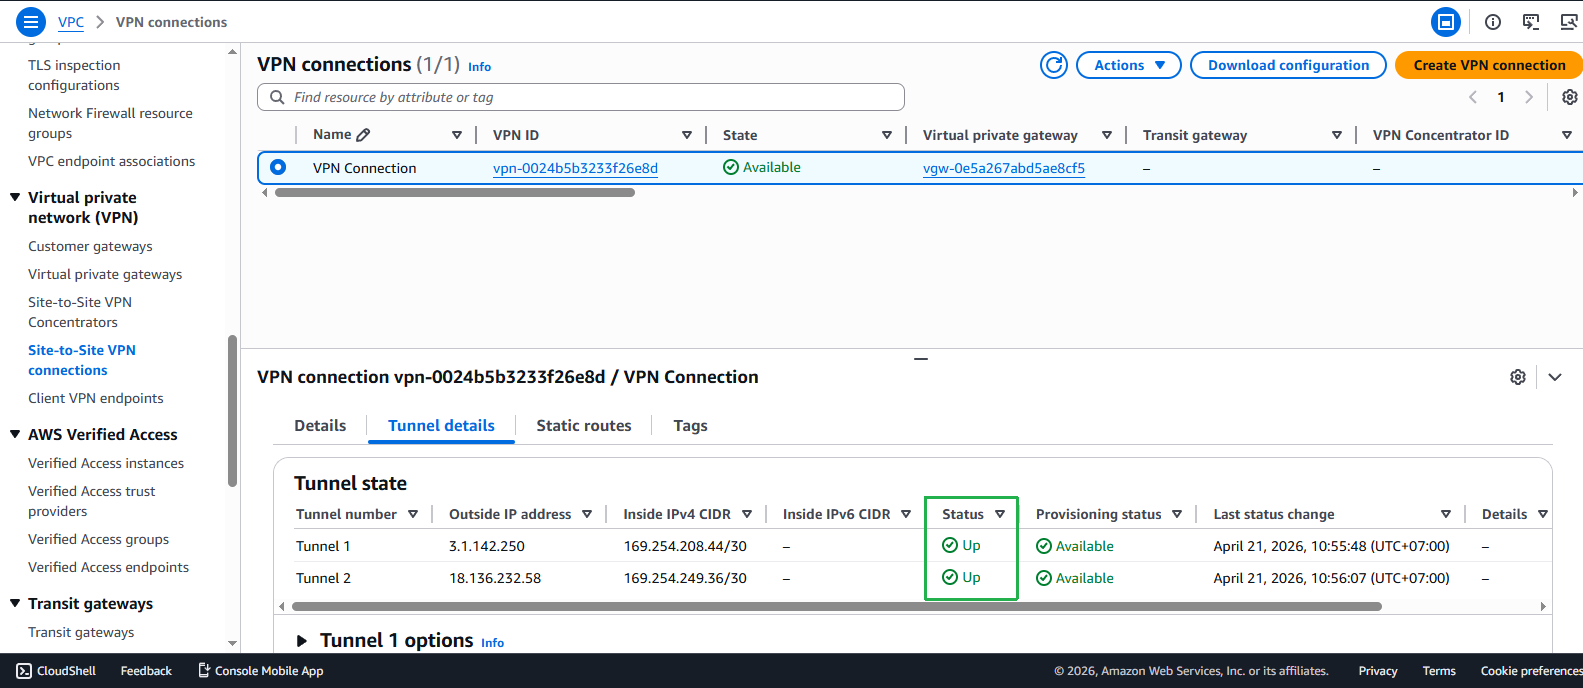

- Ensure both tunnels are UP

Advanced Tunnel Customization Options
Security Enhancement Options
💡 Recommended Security Settings:
- IKE Version: Use IKEv2 for better security and performance
- Encryption: AES-256-GCM for authenticated encryption
- Integrity: SHA2-384 or SHA2-512 for stronger hash functions
- DH Groups: Use groups 19, 20, or 21 for elliptic curve cryptography
Performance Optimization
🚀 Performance Tuning:
- DPD Timeout: Reduce to 10-15s for faster failover detection
- Rekey Margin: Set to 3-5 minutes for smooth key rotation
- Replay Window: Increase for high-throughput connections
Monitoring and Alerting Setup
📊 CloudWatch Integration:
# Create CloudWatch alarm for tunnel state
aws cloudwatch put-metric-alarm \
  --alarm-name "VPN-Tunnel-Down" \
  --alarm-description "Alert when VPN tunnel goes down" \
  --metric-name TunnelState \
  --namespace AWS/VPN \
  --statistic Maximum \
  --period 300 \
  --threshold 0 \
  --comparison-operator LessThanThreshold \
  --evaluation-periods 2
Troubleshooting Tunnel Modifications
Common Issues After Modification
⚠️ Potential Issues:
- Tunnel may temporarily go down during modification
- Customer gateway may need IPsec service restart
- Route propagation might be affected
Verification Steps
✅ Post-Modification Checklist:
- Verify both tunnels show “UP” status
- Test connectivity from both directions
- Check CloudWatch logs for any errors
- Validate route table entries
- Monitor tunnel metrics for 24 hours
💰 Cost Considerations:
- CloudWatch logs incur storage and ingestion costs
- Consider log retention policies (7-30 days recommended)
- Use log filtering to reduce costs for high-volume environments
🔒 Security Best Practices:
- Enable logging for compliance and audit requirements
- Use structured JSON format for better log analysis
- Set up automated alerts for authentication failures
- Regular review of tunnel activity patterns
💡 Customizable Tunnel Options:
- DPD Timeout: Dead Peer Detection timeout (default: 30s)
- IKE Versions: IKEv1 or IKEv2
- Phase 1/2 Encryption: AES128, AES256, AES128-GCM-16, AES256-GCM-16
- Phase 1/2 Integrity: SHA1, SHA2-256, SHA2-384, SHA2-512
- Phase 1/2 DH Groups: 2, 14, 15, 16, 17, 18, 19, 20, 21, 22, 23, 24
- Startup Action: add (default) or start
🔍 CloudWatch Logs Use Cases:
- Troubleshoot tunnel connectivity issues
- Monitor tunnel state changes
- Audit VPN activity for compliance
- Analyze traffic patterns
- Alert on tunnel failures
⚠️ Important Info: Ensure both tunnels are fully operational to maintain secure connection and high availability between AWS and your on-premises environment.
✅ Completed: VPN tunnels are configured with logging and monitoring!